Flow Hunter
Network Traffic Analyzer
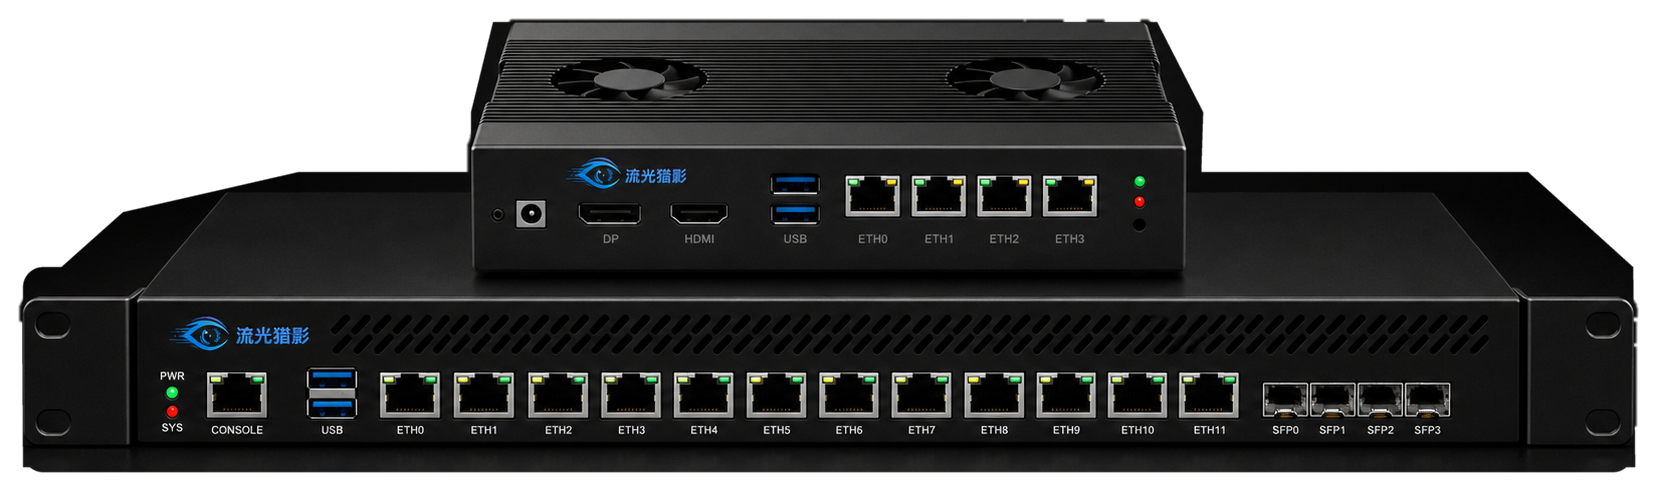
A traffic analysis appliance for network operations. Passive capture, L2-L7 analysis, historical investigation and PCAP forensics turn slow networks, choppy meetings, failed connections and abnormal bandwidth into host, session, protocol and packet evidence.
The product website opens separately. Use the button at the top right to return to NetAccura's home page.
Core Capabilities
From Symptoms to Evidence
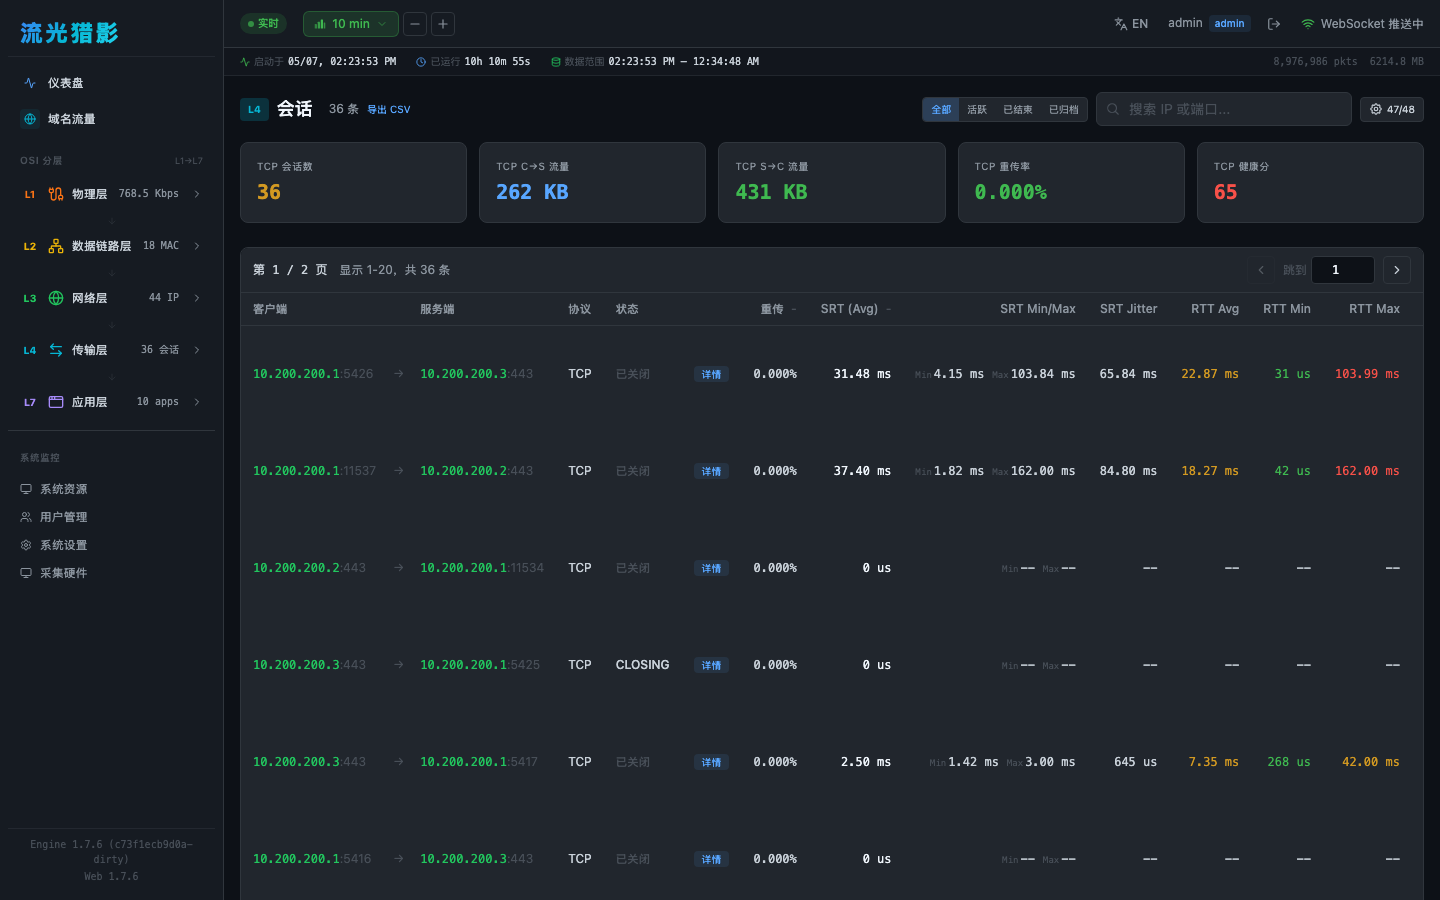
Flow Hunter brings common troubleshooting evidence into one interface: identify the affected scope, drill into protocol metrics and export the relevant PCAP.
Passive Capture
Connect through a mirrored port or TAP without inline installation. Suitable for field troubleshooting and continuous monitoring of core links.
Layered L2-L7 Analysis
Organize MAC, VLAN, IP, TCP/UDP, DNS, TLS and HTTP evidence into a searchable trail.
Quality Metric Correlation
Narrow the affected scope using RTT, TCP retransmissions, zero windows, UDP jitter, peak throughput and abnormal periods.
PCAP Forensics and Historical Analysis
Export PCAP by time window, host, session and event for Wireshark review and vendor collaboration.
Troubleshooting
For Troubleshooting That Requires Clear, Reviewable Findings
Models
From Portable Troubleshooting to Continuous Core-Link Analysis
Scout Mini
Compact Portable Appliance
Individual Engineers and Small Sites
Analyst Box
High-Performance Portable Appliance
Multi-Interface Capture, Incident Review and Delivery
Station 1U
1U Rackmount
Department-Level Permanent Analysis
Core 2U
2U Server Form Factor
Core Links and Data Centers
Visit the dedicated product website for complete interfaces and model details
This page provides the overview and site navigation. The dedicated product website retains its full design and interactions and opens separately.
Open the Flow Hunter Website