1
Create Normal Background Traffic
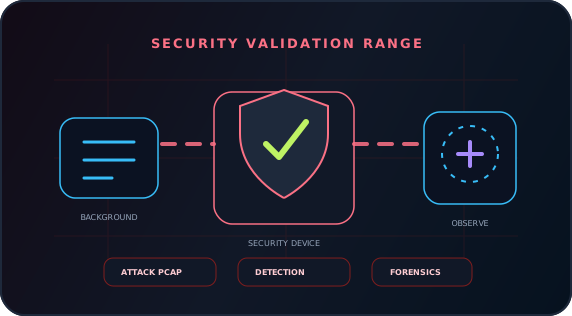
Generate background packets with varied addresses, ports, sizes and rates, or replay normal application PCAPs. Use real clients and servers when connections or full application interactions are required.
Solution Detail
Background Traffic, Attack PCAPs, Passive Analysis and Evidence Retention
Validate detection, performance, false positives/negatives and forensics under realistic background traffic, attack samples and impaired links.
Core Emulation Equipment
Optional Supporting Tools
Products
3
Scenarios
6
Evidence
PCAP
Why
Single attack packets do not represent real security environments, which include normal traffic, scans, lateral movement, DNS/HTTP/TLS sessions, bursts, jitter and policy changes. Background traffic and replayable evidence are needed to assess detection accuracy and performance.
Traffic Generation provides background generation and attack PCAP replay; simultaneous modes require separate devices. ChaosBridge adds link degradation, while Flow Hunter observes sessions and captures before/after the security appliance, connecting input traffic to response.
Topology
How
Generate background packets with varied addresses, ports, sizes and rates, or replay normal application PCAPs. Use real clients and servers when connections or full application interactions are required.
Replay attack PCAPs, malicious sessions, exploit samples, scans and historical incidents with configurable rates, loops, IPv4/port rewriting and mixing ratios.
Add ChaosBridge around the security path to emulate loss, delay, reordering and congestion. Check missed detections, incorrect blocking and performance drops.
Flow Hunter observes session changes, alerts, blocking, retransmissions and PCAPs before/after the appliance, producing a detection-path review.
Product Stack
Core Emulation Equipment
Optional Supporting Tools
NetAccura Traffic Generation
Generate L2-L3 test streams. Software models also replay Ethernet PCAPs, rewrite IPv4 addresses and TCP/UDP ports, and multiply traffic for performance, security detection and issue reproduction. Stop all transmit tasks before switching modes. Simultaneous generation and replay require separate devices.
Flow Hunter
Capture passively through mirrored ports or TAPs for L2-L7 analysis, session investigation, protocol-stage diagnosis and PCAP export.
Result
Combine normal traffic, attack samples, load and link anomalies to expose false positives, missed detections and performance issues.
Provide attack traffic, before/after sessions and PCAPs rather than relying solely on alert screenshots.
Deliver more than throughput or delay figures: include topology, parameters, timelines, quality curves, key sessions, anomalies, PCAP extracts and retest results. Development, testing, operations, vendors and customers can discuss the same evidence rather than relying on screenshots, verbal descriptions and repeated debate.
References
Next Step
NetAccura can create a test topology, parameter table and POC plan based on your links, models, application protocols, available PCAPs and SLA goals.